Cybersecurity & IT Services
Enterprise-grade cyber resilience, 24/7 monitoring, and hardened Microsoft security.
Protect your business against ransomware, data breaches, and insider threats. We deliver comprehensive vulnerability assessments, secure cloud migrations, 24/7 security monitoring, and advanced Microsoft Purview, Sentinel, and EDR/XDR threat detection.
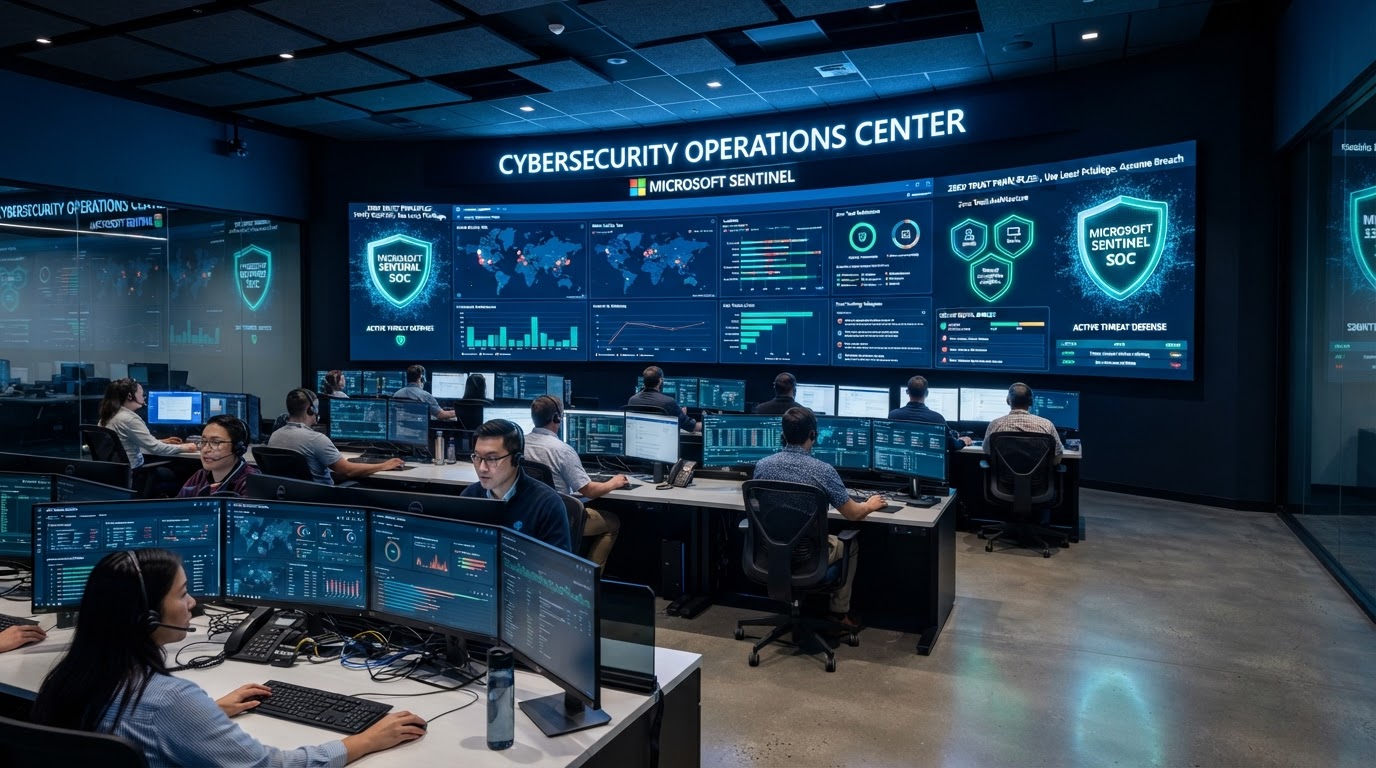
Dedicated Senior Engineering Team
Comprehensive Cybersecurity & IT Services Solutions
Every engagement is architected to enterprise operational standards, custom-configured to your organisation's scale and workflows.
Website & Web App Security
Cloudflare Web Application Firewall (WAF), DDoS mitigation, SSL/TLS hardening, automated vulnerability scans, and code-level security audits.
Security Audits & Penetration Testing
Thorough vulnerability assessments, simulated breach testing, configuration reviews, and actionable remediation roadmaps.
Cloud Setup & Migration
Hardened Azure, AWS, and Microsoft 365 cloud architecture with immutable backups, encrypted storage, and least-privilege IAM policies.
24/7 Security Monitoring & SIEM
Continuous log ingestion, anomaly detection, automated correlation rules, and active threat hunting across all corporate endpoints.
Microsoft Purview
Data loss prevention (DLP), sensitive data discovery, classification labels, information governance, and regulatory compliance posture.
Microsoft Sentinel (SIEM / SOAR)
Cloud-native security information and event management with AI-powered analytics and automated incident playbook orchestration.
EDR and XDR (Endpoint Threat Protection)
Extended detection and response powered by Microsoft Defender for Endpoint, isolating compromised devices before lateral network movement.
Plan. Deliver. Manage.
Following established international IT consultancy practices, our lifecycle ensures seamless delivery from initial architecture through continuous managed optimization.
Plan & Advise
Threat landscape assessment, security posture gap analysis, compliance scoping, and Zero Trust roadmap definition.
- Strategy & roadmapping
- Architecture validation
- Risk & compliance audit
Deploy & Transform
Deploy endpoint sensors, configure Microsoft Sentinel & Purview policies, harden firewalls, and execute initial penetration testing.
- Agile sprint delivery
- Rigorous QA & testing
- Production rollout
Manage & Optimise
Continuous 24/7 security event monitoring, patch management, monthly vulnerability scanning, and executive risk briefings.
- 24/7 SLA-backed monitoring
- Continuous security patching
- Proactive feature iterations
Demonstrated business impact
Real enterprise results delivered for organisations operating in competitive and regulated sectors.
Achieved Cyber Essentials Plus & cut phishing risk by 94%
Strategic Business Outcomes
Enterprise Technology Stack
Common questions about Cybersecurity & IT Services
What is the difference between EDR and XDR?
EDR (Endpoint Detection and Response) monitors laptops, servers, and mobile devices. XDR (Extended Detection and Response) broadens this by correlating telemetry across endpoints, cloud workloads, email, identities, and network logs for unified threat detection.
How does Microsoft Purview protect our sensitive company data?
Microsoft Purview automatically discovers, classifies, and labels sensitive data (like financial documents, PII, and customer contracts). It blocks unauthorized emailing, downloading, or USB copying based on strict policy rules.
Can you help our company achieve Cyber Essentials or ISO 27001 certification?
Yes. We guide organizations through the technical remediations, policy documentation, access controls, and submission audits required for Cyber Essentials, Cyber Essentials Plus, and ISO 27001.
Other core services
Website Development
Business websites, Shopify, WordPress & custom builds that convert.
Custom App & Software Development
Booking, delivery, CRM, ERP & business management software.
AI Agent
AI voice agents, receptionist, sales & customer service agents that work 24/7.
Business Automation
Workflow automation, WhatsApp & email automation that runs your operations.
SEO & Digital Marketing
Google SEO, Ads, social media & lead generation that grows revenue.
Ready to accelerate your technology roadmap?
Schedule a complimentary 30-minute consultation with an IOMAX solution architect to discuss requirements, timeline and strategic investment.